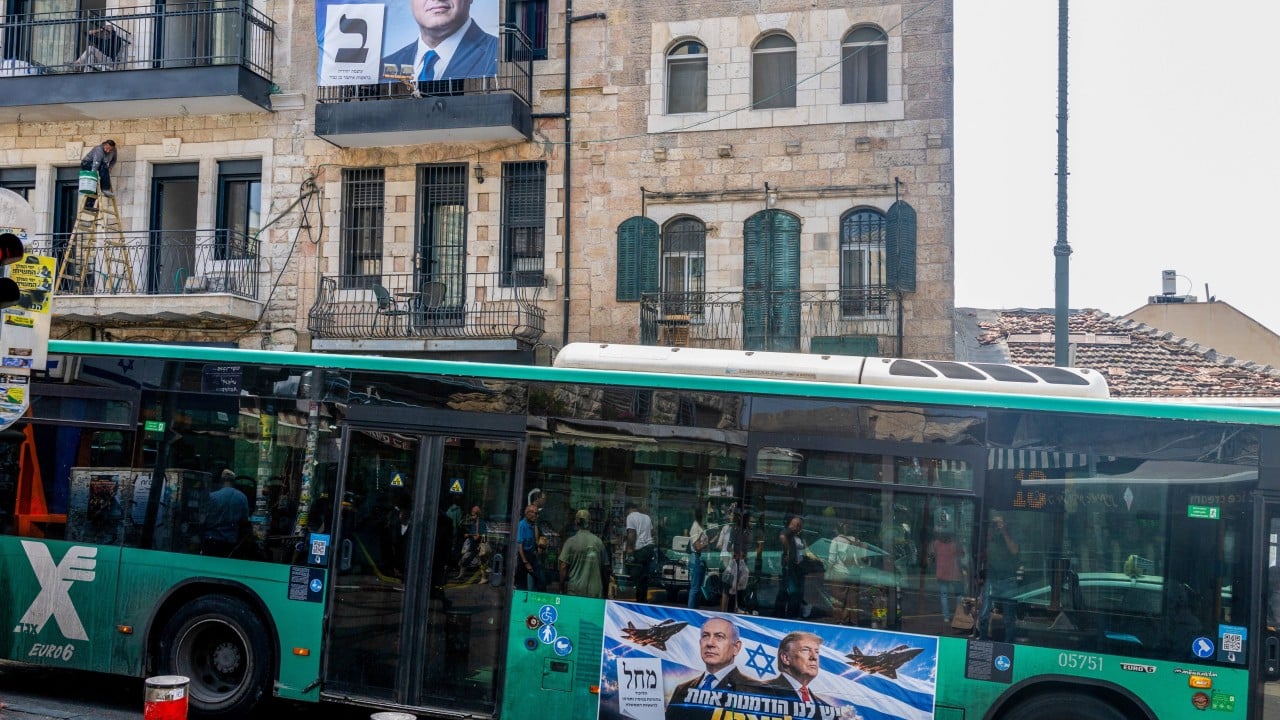
Public warnings by Israeli Prime Minister Benjamin Netanyahu regarding potential Iranian interference in Israeli elections represent a calculated shift in deterrence signaling, moving covert cyber and influence operations into the domain of overt strategic communication. Rather than serving as a routine intelligence update, this rhetoric functions as a preemptive cost-imposition strategy designed to alter Tehran’s risk calculus before an electoral cycle enters its most vulnerable operational phase. Standard geopolitical coverage treats these statements as isolated political theater or simple diplomatic friction. In reality, they reflect a structured doctrine of deterrence by denial and deterrence by punishment applied to gray-zone warfare, where the target is not physical infrastructure, but democratic legitimacy and public trust.
To understand the mechanics of this warning, one must separate domestic political utility from national security doctrine. Both operate simultaneously, yet they rely on entirely different operational levers. Recently making headlines in related news: Two Houses on the Same Hill and the Fight for Israel's Future.
The Architecture of Gray-Zone Electoral Interference
State-sponsored election interference rarely relies on altering vote tallies directly. Modern democratic voting systems—particularly those utilizing paper ballots and decentralized counting mechanisms like Israel’s—present high friction and low return on investment for direct kinetic or cyber manipulation. Instead, adversarial states execute cognitive and infrastructural disruption designed to degrade confidence in the outcome regardless of who wins.
This operational model breaks down into three distinct vectors: Additional insights into this topic are detailed by BBC News.
- Infrastructural Friction and Denial of Service
Adversaries target peripheral digital infrastructure rather than core tallying systems. Distributed Denial of Service (DDoS) attacks against municipal websites, voter registry lookup portals, and media outlets create the perception of systemic failure on election day. The objective is psychological: if a citizen cannot verify their polling station online, they are primed to believe the physical voting process is compromised. - Information Laundering and Polarization Amplification
Rather than fabricating narratives from scratch, state actors identify existing socio-political fractures within the target electorate and inject algorithmic amplification. In the Israeli context, this involves exploiting deep-seated divisions over judicial reform, military conscription, coalition politics, and security policy. By operating networks of inauthentic accounts across Telegram, X, and Facebook, external actors widen the epistemic gap between rival voting blocs, ensuring that the losing side views the eventual government as illegitimate. - Doxxing and Asymmetric Leaks
Hack-and-leak operations serve to disrupt campaign momentum and force political leadership into reactive crisis management. Exfiltrating data from political party servers, campaign managers, or prominent public figures—and releasing that data selectively—creates asymmetrical media cycles. Even when the leaked material contains no criminal wrongdoing, the breach itself signals vulnerability and erodes institutional authority.
The Mechanics of Preemptive Deterrence Signaling
When a head of government issues an explicit warning—"don't test us"—directed at an adversarial intelligence apparatus, the statement executes two strategic functions simultaneously. First, it establishes a public red line that raises the political cost of inaction if an attack occurs. Second, it signals to the adversary that their operational security has already been compromised.
Deterrence by Attribution
Covert influence operations depend on plausible deniability to remain effective. Once a narrative is exposed as foreign manipulation, its persuasive power collapses among the target audience. By publicly forecasting Iranian interference, Israeli intelligence and political leadership pre-bunk future leaks or viral disinformation campaigns. If a major hack-and-leak operation occurs three weeks prior to voting, the public framing is already established: the material is an Iranian intelligence product, not an organic domestic scandal. This neutralizes the informational payload before it is deployed.
Escalation Dominance in the Cyber Domain
The phrase "don't test us" invokes the concept of cross-domain escalation. Historically, Israel has maintained a policy of strategic ambiguity regarding its offensive cyber capabilities, punctuated by high-visibility retaliatory strikes against Iranian infrastructure—such as disruptions to fuel distribution networks and port facilities. Warning Tehran against electoral meddling communicates that gray-zone interference will not be met with proportionate, low-level cyber responses. Instead, Israel reserves the right to escalate vertically, targeting critical Iranian economic or energy infrastructure in retaliation for interference in its domestic political process.
The Intelligence Paradox
Issuing a public warning carries an inherent operational trade-off. To make the threat credible, leadership must demonstrate awareness of the adversary's intent, which risks alerting the adversary to specific intelligence collection methods. Security apparatuses must balance the tactical value of monitoring an adversary's network quietly against the strategic value of disrupting their timeline through public exposure. When leadership chooses public exposure, it indicates an assessment that the adversary's operations are moving from reconnaissance to active execution, making disruption the priority over continued observation.
Domestic Political Utility and Principal-Agent Dynamics
Analyzing national security rhetoric in isolation ignores the domestic political incentives of the speaker. In any parliamentary democracy, security warnings issued by an incumbent prime minister interact directly with domestic electoral dynamics.
- The Rally-Around-the-Flag Effect: External threats historically consolidate support around incumbent leadership, shifting voter focus from domestic economic or social grievances to national security competence. Framing the upcoming election as a battleground against a foreign existential adversary elevates the political salience of security credentials.
- Delegitimization of Opposition Narratives: A structural risk of preemptive interference warnings is their potential misuse in domestic political discourse. When foreign interference becomes an established premise, any damaging leak, grassroots protest, or sharp critique of the government can be dismissed by political allies as the result of foreign manipulation. This creates an epistemic shield that complicates legitimate journalistic scrutiny and opposition campaigning.
- Institutional Friction: Intelligence agencies (such as the Shin Bet and the National Cyber Directorate) operate on empirical risk assessments, while political leaders operate on electoral incentives. The convergence of an intelligence assessment warning of foreign cyber activity with a prime minister's campaign messaging does not invalidate the underlying threat, but it alters how that threat is communicated to the public.
Operational Limitations of Public Warnings
Strategic signaling is not a self-executing defense mechanism. Relying on public deterrence to secure an electoral cycle introduces distinct vulnerabilities that must be managed through technical and institutional controls.
First, attribution thresholds remain porous. State actors routinely outsource cyber and influence operations to proxy groups, criminal syndicates, or hacktivist fronts to obscure state sponsorship. If an Iranian-backed proxy executes a disruptive ransomware attack against a major Israeli logistics firm during election week, Tehran can deny direct state involvement. A rigid red line risks forcing the defending state into a dilemma: either retaliate against Tehran based on classified intelligence that cannot be publicly verified, risking international diplomatic friction, or withhold retaliation and suffer a loss of deterrence credibility.
Second, domestic amplification cannot be deterred externally. Foreign influence operations only succeed when domestic actors—politicians, media personalities, and citizens—willingly amplify the injected narratives. Deterrence aimed at Tehran does nothing to stop domestic partisan actors from repeating foreign-seeded disinformation because it aligns with their immediate political goals.
Third, over-warning induces alert fatigue. If intelligence agencies and political leaders repeatedly warn of catastrophic foreign interference that fails to materialize in a visible way, the public discounts future warnings. Credibility in strategic communication requires precision; broad, recurring alarms degrade public trust almost as effectively as the interference itself.
Hardening the Electoral Perimeter
Securing a democratic election against sophisticated state-sponsored gray-zone operations requires shifting resources from rhetorical deterrence to structural resilience. National security apparatuses and electoral commissions must execute a three-part defensive posture:
- Air-Gap Critical Infrastructure and Isolate Peripheral Portals: Maintain strict physical and digital separation between vote-tabulation systems and public-facing informational websites. Deploy aggressive DDoS mitigation and static fallback pages for voter registries so that even a sustained volumetric attack cannot prevent citizens from finding their polling locations.
- Establish Pre-Agreed Attribution Protocols: Intelligence agencies, rather than political offices, must own the public attribution of foreign interference. Establishing an independent, apolitical technical council to verify and announce foreign cyber intrusions prevents security warnings from being perceived as partisan campaign tactics, preserving public trust in the alerts.
- Enforce Platform Transparency and Rapid Takedown: Mandate real-time data sharing between social media platforms and national cyber defense units regarding coordinated inauthentic behavior. Reducing the dwell time of foreign bot networks from days to hours denies adversarial narratives the algorithmic momentum required to cross over into mainstream domestic media.
Deterrence statements establish the strategic boundary, but technical hardening and institutional independence determine whether that boundary holds under pressure.


